A small business can have a strong front-door lock and still leave an important online account protected by a password alone. That account might be the owner’s email, the bookkeeping service, or the administrator login that controls everyone else’s access.
For a Connecticut Shoreline shop, professional office or small service business, the useful question is where to begin. You do not need to change every account in one afternoon. Start with the accounts whose loss would interrupt work or give someone control over other services, then make sure the business can recover access.
What MFA actually adds
Multifactor authentication, usually shortened to MFA, requires more than a password to establish that you should be allowed in. Depending on the service, that might involve an authenticator app, a security key or another supported method. The FTC recommends MFA for protecting sensitive business information.
Entering a second password or answering another knowledge question is not the same as adding a different kind of factor. Nor does installing an authenticator app automatically protect every business account. Each service needs its own supported enrollment and, where applicable, an administrator’s enforcement setting.
Think of this as an account-by-account project with a clear owner, rather than an app to install and forget.
Start with email and accounts that control other accounts
Our recommended first group is business email and the accounts used to administer your email service. Email often sits at the center of customer correspondence, password resets and everyday approvals. Ask what someone could reach if they controlled that mailbox.
Next, review the identities with authority over the business’s technology: cloud-service administrators, the password manager, website and domain administration, and remote-access services. An account used only occasionally may still deserve early attention if it can change other people’s access.
For a small Shoreline business where the owner also handles technology, write down which login does what. Avoid assuming that the address used for ordinary correspondence is the only account that matters. This is prioritization advice, not a claim that any particular local business has been attacked.
Then cover money, records and daily operations
Review banking, payment processing, payroll, bookkeeping and the services holding important business files. The exact order should follow your business: a retailer and a design studio may depend on different systems.
Make a short working list with four columns:
- Service and business purpose.
- Person responsible for access.
- Available authentication methods and whether protection is enforced.
- Recovery arrangements and the date they were checked.
Keep passwords and recovery secrets out of that list. Its purpose is to show coverage, not become another place to expose credentials.
This approach follows the broader risk-management principle in NIST’s Small Business Quick-Start Guide: understand the systems and services the business relies on, then prioritize protection around its needs.
Choose the strongest practical supported method
Different MFA methods provide different protection. A code or approval prompt can add a useful hurdle, but a convincing fake sign-in page may still trick someone into providing a code or approving an attacker’s login.
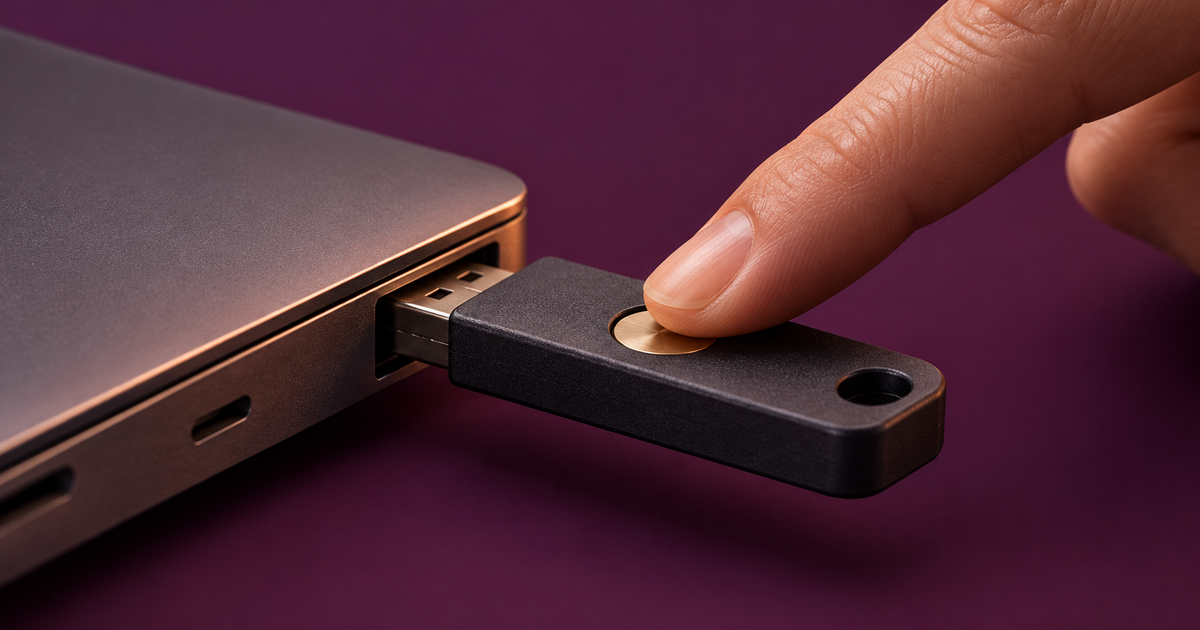
Where your service and business policies support them, consider phishing-resistant options such as FIDO2 security keys or passkeys. The UK National Cyber Security Centre explains why traditional codes and push approvals remain vulnerable to phishing, and recommends passkeys where supported, with two-step verification where they are not.
A passkey can replace the typed password rather than simply add another code. Microsoft’s passkey explanation describes how the credential is associated with the legitimate service and unlocked using the device’s supported verification, such as a PIN or biometric check.
You do not need to buy a security key before reviewing your accounts. First establish what each provider supports, what your devices can use, and how recovery works. Avoid assuming that one method or one set of instructions applies to every bank and cloud service.
Plan for a lost phone before it happens
Protection that depends entirely on one employee’s phone creates a continuity problem when that phone is replaced, lost or unavailable. Ask who can help restore access and what the provider requires.
For Microsoft work or school accounts, Microsoft directs users to their Security info page to add methods supported by their organization, and recommends registering multiple sign-in methods. Available options depend on the organization’s policy.
Before removing an old method, confirm that its replacement works. Secure any recovery codes a provider issues, and keep the recovery process under business control. Do not put those codes in a shared planning document or send them around by email.
An owner-operated office should also discuss administrator recovery with its IT provider. The aim is continued business access without sharing one person’s everyday login among several people.
Make the first change small enough to finish properly
Choose one important account and a time when its owner can complete setup without interrupting customer work. Open the service through a trusted bookmark or its known address. Review the available method, enroll it, test the intended sign-in process and document the recovery arrangement.
Then expand to the next account. Check that the people who need protection are actually enrolled; an available feature and an enforced policy are different things.
Keep software updates, unique passwords where passwords remain in use, and staff awareness in the plan. MFA reduces important risks, but it does not make an unsafe device or every fraudulent request harmless. Never approve a sign-in you did not initiate just to make a prompt disappear.
If you would like help deciding where to start, Lyme PC Repair’s business IT services support Connecticut businesses with practical technology planning. Contact us to review your important accounts, supported sign-in methods and recovery arrangements before making broad changes.